Diplomacy
Anthropic uncovers Claude use by Iranian, Houthi, and Russian units


Artificial intelligence company Anthropic has disclosed attempted “abuses” of its Claude AI model ranging from conventional weapons to biological research by state-linked entities, foreign intelligence services, and cybercrime networks, publishing the findings in a detailed threat intelligence report.
A significant portion of the report comprised the development of guided missile software by the Houthis in northern Yemen and the conversion of the model into a military reconnaissance tool by Iran-linked actors seeking to target US naval assets in the Middle East.
Covering the period between December 2025 and August 2026, the report shared details of activities detected across seven primary areas: cyberattacks, influence operations, mass surveillance, conventional weapons development, biological risks, and unauthorised model distillation.
The company announced that it had terminated all accounts violating its rules and shared the resulting data with relevant international counterparts.
According to findings by Anthropic’s Threat Intelligence unit, a weapons cell based in northern Yemen, where the Houthis operate, substituted human software engineers with the Claude Code system across three distinct missile development programmes.
These efforts comprised a tactical rocket equipped with a terminal guidance system powered by a commercial smartphone processor, a multi-stage ballistic missile with a target range exceeding 2,000 kilometres, and missile designs carrying a hypersonic glide vehicle.
The cell utilised the artificial intelligence to adapt open-source autopilot software to the smartphone processor, optimize flight control algorithms, and compile firmware.
Structuring their Claude accounts like a virtual engineering team, the Houthis assigned one account to write code, another to conduct research, and a third to review and audit the written code.
The report noted that the group conducted an actual test launch with a guided rocket in the Yemeni theatre.
Immediately following the failure of the live-fire test, the actors were documented returning to the Claude platform within hours to upload telemetry data and diagnose the cause of the malfunction.
The cell was observed successfully compiling offline simulation tools capable of operating independently even if access to Claude were severed.
We're publishing our most detailed threat intelligence report to date.
It covers how people tried to misuse Claude—for cyberattacks, influence operations, surveillance, biology, and building weapons—and how we found and stopped them.
We disrupted every operation in the report,…
— Anthropic (@AnthropicAI) September 10, 2026
Iran tracked US warships and personnel
Another military case detailed in the report involved attempts by Iran-linked cyber actors to target US naval forces in the Middle East.
These actors were found to have scraped open-source military data to draft operational targeting manuals directed against American warships and personnel.
Iran extracted name rosters of American military personnel from the captions of publicly accessible military photographs, monitored vessel and aircraft transponder data, authored code to scan commercial satellite imagery, and mapped vulnerabilities in maritime satellite communication terminals.
Other networks linked to the Tehran government were determined to have developed domestic and regional surveillance systems. A Qom-based unit produced a malicious web browser extension disguised as a prayer-time application to harvest credentials from social network users, funneling the data into a central case management system designated “Arman”.
Additionally, official Iranian institutions reportedly cloned authors’ voices using AI and operated multilingual disinformation networks to lay the groundwork for the supreme leadership succession.
Russia also used it for an autonomous kamikaze drone swarm
The report stated that an independent Russia-based software team developed fully autonomous kamikaze uncrewed aerial vehicle swarm software dubbed “DronDoc” or “Serafim”.
Affiliated with a university connected to the Russian Academy of Sciences, the team was said to have trained the artificial intelligence to distinguish between friendly and hostile elements using footage retrieved from the Ukrainian battlefield.
The developed system was designed with the capability to select targets, execute live human classification, and issue detonation commands without requiring human intervention, with simulations run directly against coordinates in the Donetsk region.
Meanwhile, the Russian-origin “Midnight Blizzard” group targeted the Ukrainian drone supply chain and staged attacks aimed at foreign officials and drone engineers by compromising hotel Wi-Fi networks.
A procurement manager stationed at a design bureau in Moscow was also discovered drafting plans via Claude to circumvent European sanctions. The individual was recorded assembling fraudulent tender and logistics correspondence to transport German-made magnetometers, space-grade photovoltaic sheets, and military aviation oxygen systems into Russia through intermediary firms based in China and Hong Kong.
Biological threats and pathogen engineering
The report disclosed five concrete cases regarding the deployment of artificial intelligence in hazardous biological research. Virologists attached to a military research institute were documented using AI for gain-of-function research aimed at enhancing the transmissibility and immune-evasion capabilities of the mosquito-borne Chikungunya virus.
Similarly, experimental designs were prepared to adapt the H5 avian influenza variant, which carries a 50% mortality rate in humans, to mammals and confer airborne transmission capabilities, while immune-evasion mechanisms of pathogens from the smallpox virus family were modelled.
The identities of paralytic neurotoxins subject to export control lists and haemorrhagic fever virus proteins featured on the World Health Organization’s priority epidemic list were deliberately masked and submitted to the AI for analysis.
In addition, a consultant working on behalf of the Malian State Intelligence Service designed a mass surveillance platform designated “Lakana 360” with the assistance of Claude.
The system was designed to monitor approximately 25 million SIM cards registered across three mobile operators in the country without requiring court orders, intercept audio recordings, and cross-reference records with biometric databases.
Separately, leading Chinese artificial intelligence firms including Alibaba, Moonshot, DeepSeek, Zhipu, and Xiaomi were alleged to have initiated hundreds of millions of unauthorised sessions to extract the logical reasoning chains of Claude models. Moonshot and DeepSeek platforms reportedly routed their own users’ queries secretly through Claude, in the process exposing Chinese police surveillance feeds from hundreds of cameras covering military facilities in Chengdu, internal credentials of Chinese state-owned enterprises, and live database access codes connected to the Russian Defence Ministry to third parties.
Türkiye detail in the report
The report also detailed cases involving the abuse of the Claude AI model, incorporating findings concerning an Istanbul-based technology firm.
In case GTG-84005 of the intelligence report, an operation aimed at commercial election manipulation targeting voters in Malaysia was intercepted.
According to the findings, the operation operated under the guise of a startup providing cyber intelligence and counter-disinformation tools. Anthropic determined that Istanbul-based BBS Bilisim Teknolojileri was behind the infrastructure.
According to documents, the company marketed the architecture as a paid influence operation service styled as a “military-grade, AI-powered, real-time political operations ecosystem”.
Managing roughly 1,000 synthetic X accounts, the system processed demographic and electoral data across 222 parliamentary constituencies in Malaysia, calibrating targeting around sensitive social fault lines including ethnicity, religion, and the monarchy.
The network also circulated content from Russian and Chinese state media masquerading as independent Malaysian news via an artificial media outlet designated “Malaysia Pulse”, while manufacturing fraudulent intelligence dossiers targeting an opposition politician and civil society organisations.
Anthropic reported that the network received a request to generate 1 million artificial impressions in support of the Malaysian Prime Minister and sought to secure a contract with the country’s national communications regulatory authority.
While no evidence emerged that the undertaking succeeded, the associated user accounts were closed and operational digital indicators were shared.




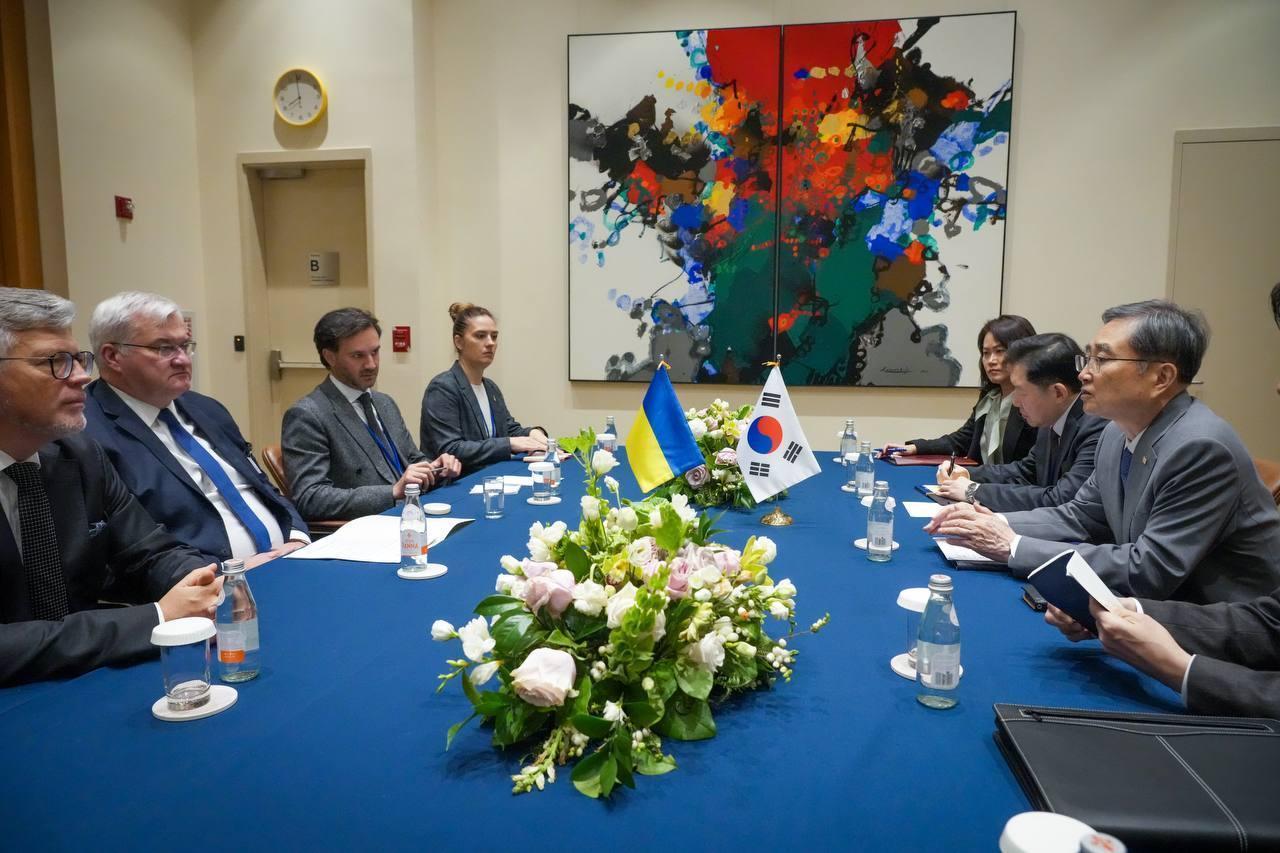
The South Korean government has decided to withdraw part of its embassy staff from Ukraine.
According to the Yonhap news agency, Foreign Ministry spokesman Park Doo-sun cited the Kyiv administration’s failure to take “positive steps” in the dispute that began with the leak of information concerning the handover of North Korean prisoners of war as the justification for the move.
The spokesman also listed the ongoing threat of air strikes, which complicates the safety of diplomats, among the reasons.
Following the withdrawal of part of the personnel, essential diplomatic contacts will continue under the leadership of the charge d’affaires ad interim to Ukraine. All consular staff tasked with protecting South Korean citizens will remain in Ukraine.
Prior to this move, the Seoul administration decided on 8 October to withdraw its ambassador. The Foreign Ministry stated at the time that it was ready to continue consultations with Kyiv to resolve the emerging issues constructively.
Tensions between the two countries began with a speech delivered by Ukrainian President Volodymyr Zelenskyy at the United Nations General Assembly in September.
Zelenskyy announced that two captured soldiers from the North Korean army had been handed over to South Korea.
South Korean President Lee Jae-myung, meanwhile, accused Kyiv of breaching a confidentiality agreement.
Lee said the disclosure of this information endangered the prisoners’ families and stability on the Korean Peninsula.
Seoul expects a public apology
Dmytro Lytvyn, an adviser to the Ukrainian president, denied the existence of a confidentiality agreement.
The South Korean Foreign Ministry summoned Ukrainian Charge d’Affaires Andriy Veshkin on 28 September and issued a note of protest against Lytvyn’s remarks.
President Lee Jae-myung warned in a statement on 2 October that they would take additional measures against Kyiv if Ukrainian authorities did not acknowledge the agreement and make a public apology. Lee stated that Ukraine itself had initially requested that the transfer of the prisoners be kept confidential.
Ukrainian Foreign Ministry spokesman Heorhii Tykhyi said the dispute stemmed from differing interpretations of the confidentiality regime.
Tykhyi noted that Seoul, based on its constitution which recognises the entire Korean Peninsula as its own territory, requested that the prisoners be handed over “like its own citizens”.
Describing the handover as a “gesture of goodwill”, Tykhyi stated that they were conducting closed-door negotiations to resolve differences of opinion.
Ambassador Park Ki-chang returned to Seoul on 10 October. According to a report by The Korea Times newspaper citing the ministry, recalling the ambassador served as a diplomatic protest against the leak of information regarding the prisoners.
The newspaper wrote that South Korea had last taken a similar step in 2008 by withdrawing its ambassador to Japan.
Moscow warned foreign diplomats
On 3 October, the Russian Foreign Ministry reiterated its warning to foreign nationals, including diplomatic mission staff, against remaining in Ukraine.
The ministry recalled its advice to leave Kyiv, citing ongoing strikes against military targets.
The ministry noted that those who failed to heed the warnings would bear responsibility for the potential consequences.
Kremlin spokesman Dmitry Peskov said in a statement on 24 September that they had no information regarding Kyiv handing over two North Korean prisoners of war to Seoul.
Peskov, noting that prisoner matters fall under the authority of the Defence Ministry and intelligence services, said, “Contacts through the special services are continuing.”
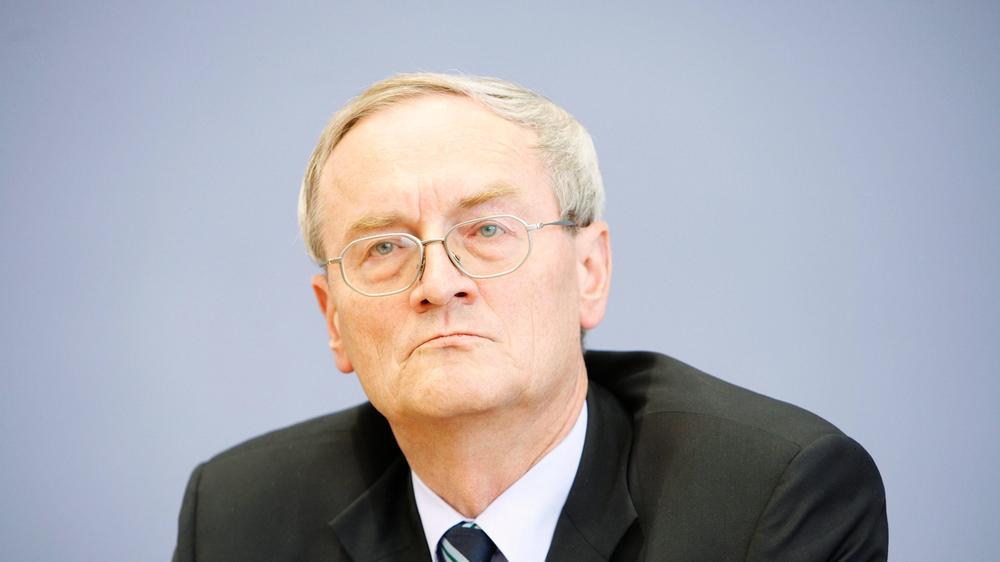
August Hanning, who led Germany’s Federal Intelligence Service (BND) between 1998 and 2005, was arrested on 6 October on allegations that he obtained roughly 2,000 classified agency documents and used them during contacts with intelligence officers from a foreign state.
Accused of high treason and espionage on behalf of a foreign intelligence agency, the former spy chief is alleged to have procured the documents from former BND employee Manfred D.
Prosecutors stated that the leaked records included internal briefing notes presented to senior German officials, though the Berlin government has not yet publicly disclosed which country received the classified data.
According to an exclusive report by Jake Green for The Cradle, seized email exchanges revealed extensive ties between the arrested Hanning and former Mossad director Danny Yatom.
The correspondence shows that the two former intelligence directors built an ongoing network of contacts following their public service, combining commercial ventures, efforts to secure political influence, and intelligence links.
This dynamic has triggered debate that using personal connections and official access for private gain has left Germany’s intelligence apparatus vulnerable.
Intelligence notes for 10,000 euros and campaign proposals
According to the reviewed emails, Hanning told Yatom in a 2018 message that he could prepare an “overall assessment based on information obtained from senior German officials and intelligence agencies” concerning an unidentified candidate.
The former BND head committed to completing the report by 13 July in exchange for 10,000 euros.
Contacts between the two men subsequently expanded to cover domestic political processes in Germany. Ahead of the September 2021 federal election, Yatom asked Hanning to approach leading candidates.
Describing CIY Global as a “political campaign company”, the former Mossad chief noted that he aimed to introduce its capabilities to German politicians, and he mentioned his intention in the same exchange to transfer documents concerning a cybersecurity firm.
Cybersecurity partnership and surveillance operations across Europe
The partnership between Yatom and Hanning reached beyond political lobbying initiatives into the cybersecurity sector.
Hanning reportedly served as a consultant for World Health Energy Holdings, a cybersecurity company linked to Yatom.
Firms of this type, established or managed by former intelligence personnel, provide commercial platforms on the international market for Israeli-origin surveillance, cyber intelligence, and political influence capabilities.
The operational presence of private Israeli-based surveillance technologies across Europe has recently entered judicial records through scandals in Poland, Spain, and Greece.
Polish prosecutors announced on 12 October that data collected under the previous government via Pegasus spyware against political opponents had been transferred out of the country, adding that manufacturer NSO Group maintained access to the technical infrastructure.
In Spain, the 2022 CatalanGate investigation established that at least 65 people, including politicians, lawyers, and civil society representatives, were targeted using Pegasus or Candiru software, with Citizen Lab researchers publishing strong evidence linking the operation to Spanish authorities.
In Greece, the surveillance operation targeting journalist Thanasis Koukakis and Member of the European Parliament Nikos Androulakis was determined to have used Predator software, linked to Intellexa, a company founded by former Israeli intelligence officer Tal Dilian.
In the German espionage investigation, the traffic between Hanning and Yatom involving paid reporting, contacts with electoral candidates, and commercial partnerships does not yet provide conclusive legal evidence regarding the final destination of the roughly 2,000 classified documents.
Nevertheless, the disclosed correspondence gives German investigators a concrete line of inquiry to assess whether classified state secrets reached commercial networks tied to Israeli intelligence.
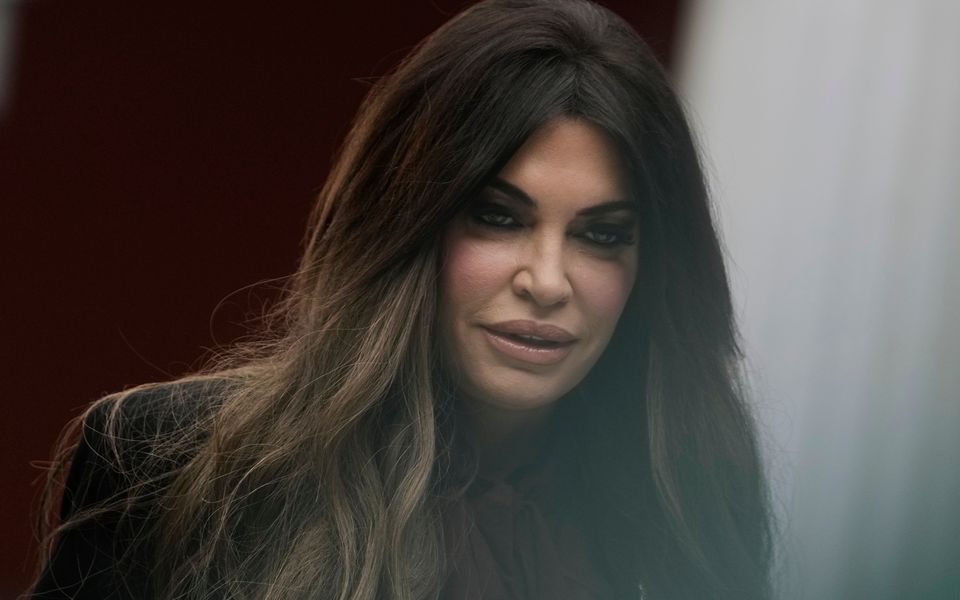
US President Donald Trump has dismissed Kimberly Guilfoyle, the US ambassador in Athens, following serious press reports concerning her conduct.
White House Press Secretary Katie Zacharia told reporters during her first briefing that Guilfoyle had been asked to resign.
“She was doing a good job, but we didn’t like what we read in the press,” Trump said. “She was not a member of my family. I think she dated my son a long time ago.”
In a social media post, Guilfoyle stated: “These claims are unfounded, and I will resolutely defend my name, reputation, and integrity.” She added that she was particularly proud of the embassy’s work.
According to Kathimerini, her removal came as no surprise in Washington. Days of successive disclosures and vigorous exploitation of the matter by Democrats had been inflicting political damage on the White House ahead of the sensitive midterm elections.
The US State Department was instructed not to comment, with crisis management transferred entirely to the White House.
Reports indicate that most of the president’s team swiftly favoured Guilfoyle’s dismissal, while Secretary of State Marco Rubio was reportedly uneasy with the demonstratively warm public welcome she had staged for him.
Democrats on the House Foreign Affairs Committee have called for an investigation.
“Her resignation does not absolve her of responsibility,” the lawmakers wrote, adding: “While American families struggled to make ends meet, she used her position as a Trump administration official to enrich herself.”
Chargé d’Affaires Josh Huck will assume ambassadorial duties until a successor is chosen.
Meanwhile, Guilfoyle’s departure is expected to cause delays in agreements between Greece and the US.
These include the so-called “Rubio package”, comprising approximately $4 billion in arms deals finalised only days before the secretary of state’s arrival.
Several procedural steps still remain before the contracts can be signed.
In Athens, opposition parties are demanding answers. Dimitris Mantzos of PASOK called for a detailed briefing on the agreements reached during Rubio’s visit.

German officials urge fighter jet alliance with Sweden and Spain

US wealthy demolish multimillion-dollar mansions for land

US and Israel weigh Iran strikes after midterm vote, reports say

Pentagon plans covert spy ring for economic war on China, report says

EU reopens debate on naming envoy for Ukraine talks with Putin
-
 Europe2 weeks ago
Berlin Left Party backs Israel’s right to exist for coalition pact
-
 America2 weeks ago
How will Brazil’s presidential runoff work?
-
 Diplomacy2 weeks ago
The West is preparing for war not with Russia, but with its own people, French analyst Georges Kuzmanovic insists
-
 Russia2 weeks ago
71 EU lawmakers demand closure of Russian Houses in 15 member states
-
 Europe2 weeks ago
MI6 investigates potential leaks after former BND chief is detained
-
 Russia2 weeks ago
US and Russian figures discuss American stake in Nord Stream lines
-
 Russia2 weeks ago
Drone strike shuts down Yandex data centre in Russia’s Ryazan region
-
 America1 week ago
Trump weighs presidential memorandum to cut surging US diesel prices
